 Cubbie Points
AT&T USM
SIEM
AT&T Cybersecurity's Unified Security Management platform combining SIEM, threat intelligence, and log management.
Price$1,075+ / month
Future of SoftwareStart Survey
SIEM
AT&T Cybersecurity's Unified Security Management platform combining SIEM, threat intelligence, and log management.
Price$1,075+ / month

SIEM
Cloud SIEM and threat detection platform designed for mid-sized businesses with fast deployment.
Price$40+ / user / month

SIEM
SIEM and security management platform providing log management, threat detection, and compliance automation for mid-market enterprises.
SIEM
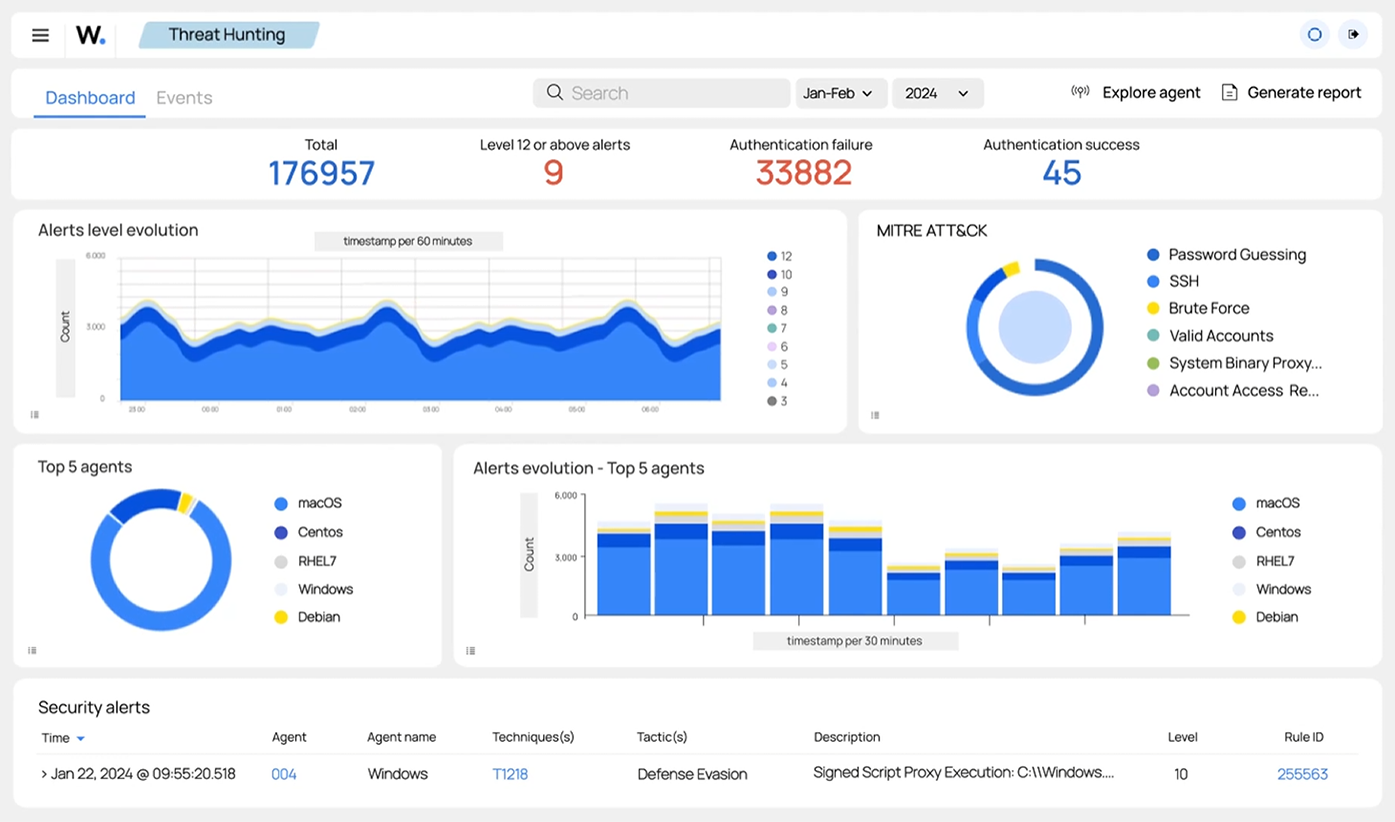
Open-source security platform providing intrusion detection, vulnerability detection, and server monitoring with SIEM integration.

SIEM
Converged SIEM platform combining security analytics, UEBA, and SOAR for threat detection, investigation, and response across IT infrastructure.
Managed Detection and Response
Managed security and detection response service providing SOC-as-a-service with integrated SIEM and endpoint protection for SMBs.
SIEM
RSA-originated network detection and SIEM platform providing real-time visibility through deep packet inspection and log analysis.

Security Information and Event Management (Expanded)
Cloud-native SIEM and UEBA platform using big data and ML for threat detection and response.
SIEM
Cybersecurity platform by N-able providing SIEM, XDR, and MDR services for midmarket companies.

SIEM
Cloud-native SIEM built for security teams to detect threats using code-based detections on real-time data.
PriceUsage-based